










Decentralized governance determines how blockchain networks and decentralized applications make decisions without relying entirely on a single executive authority. It establishes who can submit proposals, how participants express approval, what conditions a decision must satisfy, and who has the power to implement changes.
These arrangements can govern protocol parameters, treasury spending, software upgrades, risk limits, and other operational choices. However, a public voting process does not automatically mean that decision-making power is broadly distributed.
Voting rights may be concentrated among large token holders, while developers, delegates, multisignature signers, or administrators retain important implementation powers.
How the Decentralized Governance Process Works
A governance system translates a proposed change into an authorized decision. The exact process varies by protocol, but a typical on-chain governance lifecycle follows several stages.
1. Proposal creation. A participant submits a change, such as adjusting a lending protocol’s collateral parameters, funding development, or modifying a treasury allocation. The system may require a minimum token balance, delegated voting power, or another eligibility condition before accepting the proposal.
2. Review and discussion. Participants examine the proposal’s purpose, technical requirements, costs, and potential consequences. Discussions may take place in public forums before a formal vote begins. This stage matters because voters cannot assess a proposal reliably if its code, assumptions, or implementation plan remain unclear.
3. Voting-power determination. The governance contract establishes which accounts may vote and how much weight each vote receives. Some systems use token balances recorded at a particular snapshot. Others use delegated voting power or membership-based rules.
4. Approval assessment. The proposal must satisfy the applicable rules. These may include a minimum quorum, an approval threshold, a voting deadline, or additional restrictions. Quorum generally refers to the minimum participation required for a valid decision, while the approval threshold determines the support needed to pass.
5. Delay and execution. An approved proposal may enter a timelock before execution. Depending on the system, execution can occur automatically through a smart contract or require authorized signers to submit transactions. Some governance models use off-chain decisions followed by implementation by developers.
6. Verification and accountability. After implementation, participants should be able to verify whether the approved change was executed as specified. Records should make it possible to compare the original proposal, voting outcome, executed transaction, and resulting protocol state.
These stages should be evaluated separately. A proposal can pass a vote yet fail to execute, require discretionary action by an administrator, or produce an outcome different from what participants expected.
Ethereum provides a useful distinction between application-level governance and protocol-level governance. Its own protocol changes involve social, technical, and coordination processes rather than a simple token-holder vote. Many applications built on Ethereum, meanwhile, use on-chain voting mechanisms. The Ethereum governance documentation explains this difference.
Voting Power, Delegation, and Participation
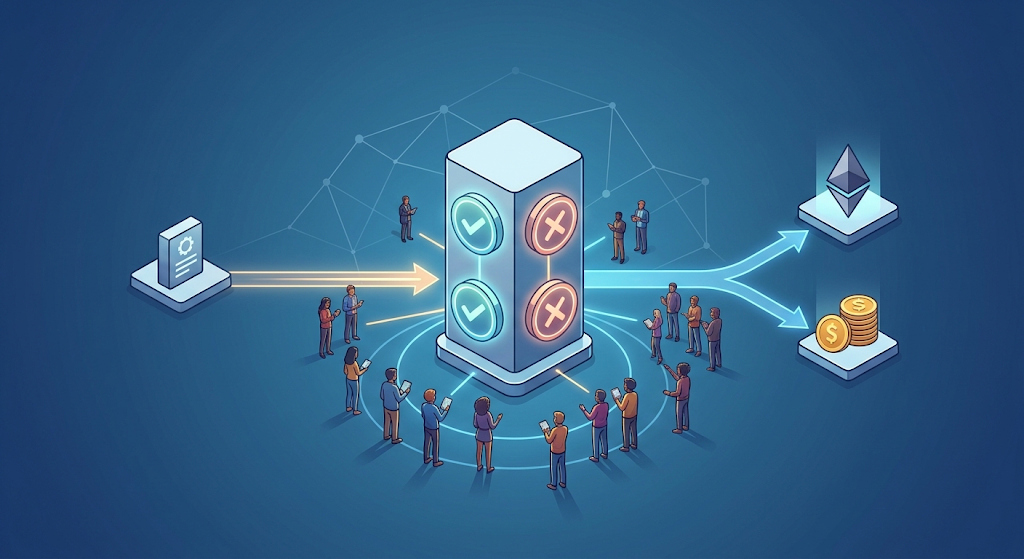
Governance rules determine whose preferences influence a decision. The design of these rules can affect participation, representation, and the likelihood that a small group controls outcomes.
Token-weighted voting
In token-weighted governance, voting influence is generally linked to the number of eligible governance tokens an account controls or represents. This approach creates a measurable relationship between token ownership and voting power, but it can also allow a relatively small number of large holders to dominate decisions.
Consider a hypothetical protocol with 10 million eligible votes. If three participants collectively control 5.5 million votes, they could determine an ordinary majority outcome when turnout is low and no additional approval constraints apply. The protocol might have thousands of token holders, yet practical decision-making could remain concentrated.
This example does not establish that concentrated voting will always produce poor decisions. Large holders may have substantial incentives to protect a protocol’s long-term viability. The limitation is that token ownership alone does not demonstrate broad representation, informed participation, or independent oversight.
Delegated voting
Delegation allows a token holder to assign voting power to another account without necessarily transferring ownership of the underlying tokens. It can help participants who lack the time or technical knowledge to evaluate every proposal.
Delegation also creates another concentration point. A small number of popular delegates may accumulate substantial influence, and token holders may not actively monitor their decisions. A governance review should therefore examine delegate concentration, voting histories, conflicts of interest, and the ease with which delegators can reclaim or reassign voting power.
Ethereum’s ERC-5805 specification describes a delegated-voting mechanism that tracks voting power over time and supports historical checkpoints. Implementations differ, so reviewers should confirm the actual rules used by each protocol.
Quorum and turnout
Quorum requirements can prevent decisions from passing with very limited participation. However, a high quorum can also make routine decisions difficult when eligible holders rarely vote. A low quorum may make governance more responsive but increase exposure to low-turnout outcomes.
Reviewers should distinguish between the number of eligible voters, the number of participating accounts, the total voting power represented, and the share of votes supporting a proposal. These measures answer different questions. A high percentage of votes in favor may still represent only a small fraction of total eligible voting power.
Free educational tool
How healthy is your hypothetical portfolio?
Seven questions about how a hypothetical portfolio is structured, with three sub-scores and an overall Health Score out of 100.
Educational tool. Results are not investment advice.
How Governance Decisions Become Executable
A vote has practical significance only when the system can translate the result into action. The execution path is therefore one of the most important parts of a governance assessment.
In an automated design, a governance contract may authorize a transaction after the proposal satisfies its voting and timing conditions. The transaction might change a protocol parameter, transfer treasury funds, or grant a contract a new permission. This approach can reduce discretionary intervention, but it does not remove the possibility of defective code, malicious proposals, or unintended consequences.
Other systems rely on a multisignature wallet. A group of designated signers must approve a transaction before it executes. This can provide an additional operational safeguard, especially when signers independently verify proposed changes. However, it also means that execution depends on the signers’ availability, security, judgment, and compliance with the governance outcome.
A third model combines voting with administrative permissions. Token holders may approve a change, but an administrator or development team may retain the ability to upgrade contracts, pause operations, or modify certain parameters. Such authority can be useful during an emergency, yet it should be disclosed and constrained.
For example, a DAO could approve a reduction in a lending market’s maximum loan-to-value ratio. The proposal passes, but implementation still requires a multisignature group to execute a transaction. If the signers delay or refuse execution, the voting result has not translated into the intended change. The governance framework should specify the signers’ authority, expected execution timeline, verification process, and escalation route.
For technical background on code execution and permissions, see What Are Smart Contracts and How Do They Shape Digital Trading?.
Governance Concentration and Capture Risks
Decentralized governance can distribute formal voting rights while leaving practical control concentrated. The relevant question is not simply how many wallets exist, but how authority is distributed across the entire decision process.
Several factors can create concentration:
- Token distribution: Large holders may possess enough voting power to determine outcomes or block proposals.
- Delegation patterns: Many participants may assign their votes to a small group of delegates.
- Administrative permissions: Developers, foundations, or designated accounts may retain upgrade, pause, or parameter-setting powers.
- Execution dependencies: A vote may require a limited group of signers or operators to take effect.
- Information asymmetry: Core contributors may understand technical consequences that ordinary voters cannot independently assess.
- Participation barriers: Transaction fees, complex proposal documentation, limited time, and governance fatigue can discourage participation.
The Bank for International Settlements has discussed the “decentralisation illusion” in decentralized finance, highlighting how governance needs and structural features can concentrate influence despite decentralization claims. Its analysis is available in DeFi Risks and the Decentralisation Illusion.
A recent study of MakerDAO governance also examined the relationship between voting-power distribution and governance outcomes. Its findings are relevant to evaluating token concentration, but they should not be treated as proof that every DAO has the same structure or faces identical risks.
Regulatory analysis also increasingly considers who can exercise effective control. The Financial Action Task Force’s July 2026 report on decentralized finance examines how control can be identified in practice, rather than relying only on labels or formal organizational descriptions. The report provides useful context for evaluating governance authority and operational responsibilities.
Common Governance Failure Scenarios
A governance framework should be assessed against plausible failures, not just its normal voting procedure.
Malicious proposal. A proposal may authorize a transfer to an unintended address, grant excessive contract permissions, or introduce a harmful parameter change. Reviewers should check whether proposal code is independently reviewed, transaction effects are disclosed, and a meaningful review period exists before execution.
Low-turnout approval. A consequential proposal may pass because most eligible holders do not participate. A quorum can reduce this risk, but its effectiveness depends on how the quorum is calculated, whether participation can be manipulated, and whether the threshold is appropriate for the decision’s impact.
Concentrated or temporarily acquired voting power. A participant or coordinated group may accumulate substantial voting influence before a proposal. Snapshot rules and voting delays can help define eligible voting power, but they do not eliminate concentration or every form of vote manipulation.
Compromised delegate or signer. A delegate’s account or a multisignature signer’s key may be compromised. The resulting risk depends on how much influence that account has and what actions it can authorize. Independent signers, hardware-backed key protection, limited permissions, and documented revocation procedures can reduce exposure.
Urgent upgrade under pressure. A vulnerability may require rapid action, creating tension between broad consultation and immediate protection. Emergency powers can help contain damage, but unrestricted authority can also be abused. A sound design defines when emergency powers may be used, who can activate them, what actions are permitted, and how the intervention is reviewed afterward.
No single safeguard eliminates these risks. Controls should be layered around proposal review, voting integrity, execution authority, monitoring, and incident response.
Free educational tool
See what a monthly contribution would have been worth
Pick an asset, set a monthly amount and a date range, and replay it against real historical prices. No forecasts.
Educational tool. Results are not investment advice.
A Step-by-Step Framework for Evaluating DAO Governance
A consistent assessment makes it easier to compare governance systems without relying on marketing claims or token-holder counts alone.
Step 1: Map the decision rights. Identify who can propose changes, who can vote, who can veto, who can execute approved transactions, and who can change the governance rules. Record any permissions held outside the voting contract.
Step 2: Measure the distribution of influence. Review voting power held by major participants, delegate concentration, historical turnout, quorum attainment, and the frequency of uncontested proposals. Where data allows, compare the largest voting blocs with the total eligible voting power. Do not assume that wallet addresses correspond to independent individuals.
Step 3: Trace one consequential proposal. Select a completed proposal that changed a protocol parameter, moved treasury funds, or upgraded a contract. Follow it from submission through discussion, voting, approval, timelock, execution, and verification. Confirm that the executed action matches the approved proposal.
Step 4: Test the safeguards. Determine whether code review, timelocks, independent signers, permission limits, monitoring, and emergency procedures are documented and operational. Check whether a privileged account can bypass the ordinary voting process and whether that authority is limited.
Step 5: Assess accountability and recovery. Review how conflicts of interest are disclosed, how voters can challenge proposals, how mistakes are corrected, and how emergency interventions are reported. Consider whether a governance failure can be contained without relying on the same individual or group whose actions caused the problem.
Step 6: Record the unresolved risks. Summarize the evidence, the control gaps, and the limitations of the available data. A transparent assessment should distinguish verified permissions and transaction history from assumptions about participant independence or future behavior.
The result should be a documented view of how governance works in practice, not a simple score based on the number of voters or the presence of a token.
Limitations and Questions to Resolve Before Relying on Governance
On-chain records can show votes, transactions, and certain contract permissions, but they do not necessarily reveal the identity of every participant, private agreements among holders, or off-chain influence over proposal development. Multiple wallets may belong to one entity, and a delegate’s voting power may not reflect independent support from every delegator.
Formal approval also does not establish that a proposal is technically sound, legally enforceable, or aligned with every stakeholder’s interests. Smart contracts execute according to their code and permissions; they do not automatically resolve disputes or interpret every unforeseen circumstance.
Legal treatment varies by jurisdiction and by the facts of the arrangement. A DAO’s name or decentralized design does not, by itself, settle questions of legal status, responsibility, or regulatory obligations. The FATF’s 2026 report is relevant to functional control and financial-crime considerations, but it is not a substitute for jurisdiction-specific legal analysis.
Institutional participants may also need to examine governance participation as an operational responsibility, including the resources required to review proposals and monitor delegated authority.
For more information, see Governance Participation as an Institutional Income Stream.
Free educational tool
Are you ready for digital assets?
Seven quick questions on knowledge, mindset and goals, with one honest answer about where you stand.
Educational tool. Results are not investment advice.
Decentralized Governance Requires Verifiable Controls
Decentralized governance is best evaluated as a complete decision system. Proposal rules determine what can be considered, voting mechanisms determine whose preferences count, and execution permissions determine whether approved decisions can take effect. Each layer can distribute authority or concentrate it.
A useful assessment therefore looks beyond public voting activity. It traces actual decisions, identifies privileged permissions, measures participation and concentration, tests safeguards against plausible failures, and records what remains uncertain. This approach provides a more grounded way to assess whether a governance structure offers meaningful accountability and whether its stated distribution of power is supported by observable mechanisms.
Explore More on Digital Asset Governance and Risk
Evaluating decentralized governance also requires staying informed about developments in digital asset markets, infrastructure, and risk management. Kenson Investments offers educational resources to help readers examine these topics and consider the mechanisms shaping digital asset networks.
Join the tribe for additional market and infrastructure insights, or contact the team to learn more.
Disclaimer: The information provided on this page is for educational and informational purposes only and should not be construed as financial advice. Crypto currency assets involve inherent risks, and past performance is not indicative of future results. Always conduct thorough research and consult with a qualified financial advisor before making investment decisions.
“The cryptocurrency and digital asset space is an emerging asset class that has not yet been regulated by the SEC and the US Federal Government. None of the information provided by Kenson LLC should be considered as financial investment advice. Please consult your Registered Financial Advisor for guidance. Kenson LLC does not offer any products regulated by the SEC, including equities, registered securities, ETFs, stocks, bonds, or equivalents.”



