










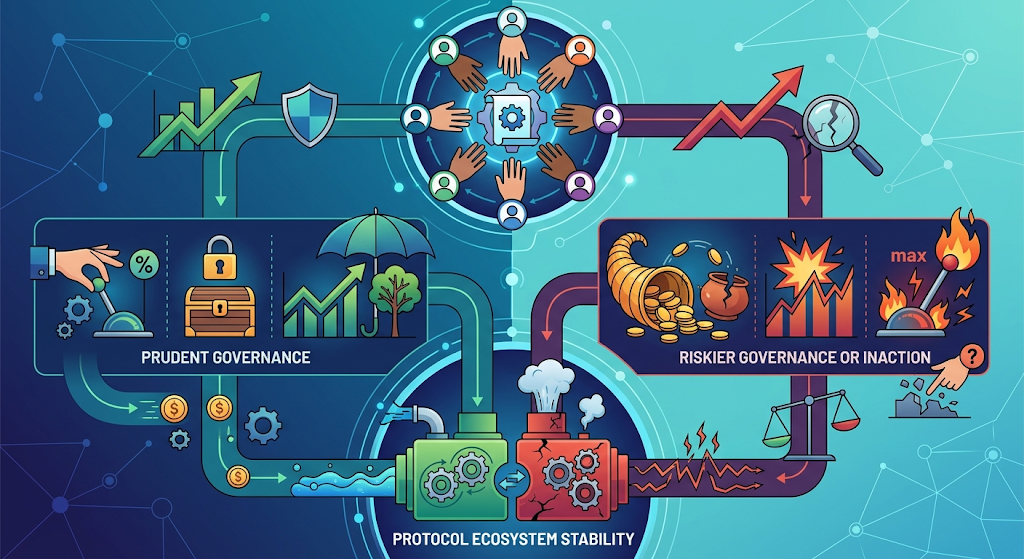
DeFi governance determines how decentralized financial protocols change their rules, manage shared resources, and respond to operational risks. Decisions can affect lending limits, collateral requirements, liquidation thresholds, transaction fees, treasury allocations, and smart contract upgrades. These choices influence how a protocol behaves under normal conditions and how it responds when markets or infrastructure come under pressure.
For this reason, DeFi governance should be evaluated as an operational control system, not simply as a voting process. A public proposal and an approved vote do not establish that a change is technically sound, that its implementation is secure, or that decision-making authority is widely distributed.
A meaningful assessment examines who can propose a change, who controls voting power, what safeguards apply before execution, and which parties retain privileged access. It also considers how a protocol detects unintended outcomes and responds when a governance decision creates new exposure.
What DeFi Governance Controls in Practice
Governance rules determine which decisions require community approval and which can be made by designated operators or administrators. The division varies by protocol, but several categories deserve particular attention.
Risk parameters. Lending and borrowing protocols may use governance to change collateral factors, borrowing limits, liquidation incentives, reserve factors, and asset-specific risk settings. These parameters influence how much users can borrow, how losses may develop during market stress, and how quickly a protocol can respond to deteriorating collateral.
Treasury allocations. Governance may authorize payments for development, security reviews, integrations, research, or other operating expenses. Treasury decisions create questions about spending limits, recipient verification, conflicts of interest, and the authority required to release funds.
Smart contract upgrades. A governance process may authorize a new implementation, modify contract permissions, or change how a protocol handles transactions. Such changes can introduce new capabilities, but they can also create vulnerabilities or alter previously understood behavior.
Emergency controls. Some protocols assign specific accounts the ability to pause markets, disable functions, or restrict activity during an incident. These powers may limit damage when time is critical, but they also create a concentration of authority that needs clear boundaries.
Market and incentive mechanisms. Governance can influence fees, liquidity incentives, reward distributions, and other economic settings. A decision that appears operationally minor may change user behavior, capital flows, and the distribution of risk across a protocol.
These responsibilities are connected, but they should not be treated as interchangeable. Voting on a treasury payment has different consequences from authorizing an upgrade to a contract that controls collateral or liquidations. The more consequential the action, the more important it becomes to understand its technical scope and execution safeguards.
How a Governance Decision Moves From Proposal to Execution
A consistent review process helps distinguish a documented decision from a change that has been safely implemented.
1. Define the decision and its intended outcome
Start by identifying the specific protocol function that will change and the reason for the proposal. A proposal to reduce borrowing capacity for a volatile asset, for example, should identify the relevant market, the existing parameter, the proposed value, and the risk condition the change is intended to address.
Broad descriptions such as “improve protocol safety” are not sufficient on their own. Reviewers need a defined objective against which the proposal can be assessed.
2. Identify who can influence approval
Examine proposal eligibility, voting rules, delegation, quorum, and approval thresholds. Determine whether voting power is concentrated among a small number of holders or delegates and whether the voting period provides adequate time for scrutiny.
Formal participation figures require context. A proposal receiving overwhelming support among participating voters may still represent a limited share of total eligible voting power.
3. Examine the technical and financial impact
Assess how the proposed change affects protocol behavior, users, liquidity, collateral, and treasury resources. For code changes, reviewers should understand the functions being modified, permissions being added or removed, dependencies involved, and tests performed before deployment.
The assessment should also consider unintended effects. Raising a collateral factor, for instance, may increase borrowing capacity while leaving the protocol more exposed to a sudden decline in collateral value.
4. Verify the execution path
Determine whether approval triggers an automated transaction or whether another party must implement the decision. Identify any multisignature wallet, administrator, development team, or external service that can delay, modify, or block execution.
Check for a timelock or review period where appropriate. Confirm whether emergency permissions can bypass ordinary governance and what constraints apply when they are used.
5. Monitor the change after implementation
After execution, compare the resulting contract state with the approved proposal. Monitor relevant risk indicators, including utilization, collateral health, liquidation activity, treasury balances, and unexpected permission changes.
The review should also establish what happens if the change behaves differently than expected. Depending on the protocol, recovery may require a corrective proposal, a limited administrative intervention, a pause, or a rollback mechanism where one exists.
Ethereum’s governance documentation distinguishes application-level on-chain voting from the broader social and technical process used to coordinate Ethereum protocol changes. That distinction matters because a DeFi application’s governance rules do not necessarily describe the governance of the underlying blockchain.
Free educational tool
How healthy is your hypothetical portfolio?
Seven questions about how a hypothetical portfolio is structured, with three sub-scores and an overall Health Score out of 100.
Educational tool. Results are not investment advice.
Example: Changing a Lending Protocol’s Collateral Parameters
Consider a hypothetical lending protocol that accepts a volatile digital asset as collateral. Governance proposes increasing the collateral factor from 65% to 75%, allowing users to borrow more against the same collateral value.
The proposal may increase capital efficiency, but it also reduces the buffer protecting the protocol if collateral prices fall. Before approval, reviewers should consider price volatility, oracle reliability, market liquidity, liquidation capacity, and the potential for correlated declines across collateral assets.
A more complete decision process would ask:
- What evidence supports the proposed parameter?
- How would the change behave during a rapid price decline?
- Can liquidators sell enough collateral without severe price impact?
- Does the protocol have reliable price feeds and defined responses to stale or abnormal data?
- Is the proposed change reversible, and how long would reversal take?
- Who can execute or override the decision after the vote?
Suppose the proposal passes, but the implementation also grants an administrator broader permissions than the proposal disclosed. The vote alone would not establish that the change was implemented safely. The additional permission must be identified and assessed separately.
This example illustrates a central governance principle: approval, implementation, and operational outcome are three separate checkpoints. Each requires its own evidence.
Governance Concentration and Administrative Control
DeFi protocols may describe their governance as decentralized while retaining important decision-making powers in a limited group. Token-weighted voting, delegate arrangements, administrator privileges, and control over software upgrades can all affect how much authority is distributed in practice.
A review should examine at least four dimensions.
Voting concentration: How much voting power is held by the largest participants and delegates? Can a small group approve or block proposals under typical turnout conditions?
Implementation authority: Does the voting result execute automatically, or does a limited group control the final transaction? Are signers required to follow a defined process, and are their permissions restricted?
Technical influence: Who develops, reviews, and deploys contract changes? Can developers introduce changes through a path that does not require the same approval as an ordinary proposal?
Emergency authority: Who can pause activity, alter critical settings, or respond to a vulnerability? Are these powers limited by scope, duration, or post-incident review?
The Financial Action Task Force’s July 2026 report on decentralized finance highlights the importance of evaluating control and influence in practice, including governance-token concentration, administrative privileges, upgrade control, and influence over development or infrastructure. The report recommends a functional, risk-based approach rather than relying only on how an arrangement describes itself.
Concentrated authority is not automatically evidence of misconduct. Emergency powers can help contain damage, and experienced contributors may be necessary to maintain complex systems. The issue is whether those powers are visible, limited, accountable, and supported by appropriate checks.
For broader coverage of proposal lifecycles, voting structures, and governance evaluation, see Decentralized Governance: The Future of Collective Decision-Making in Digital Asset Networks.
Free educational tool
Test a hypothetical allocation against history
Choose assets and weights, set contributions and costs, and review historical outcomes, volatility and drawdowns. Historical data, not a forecast.
Educational tool. Results are not investment advice.
Failure Scenarios DeFi Governance Should Address
Governance controls are most meaningful when they account for plausible failure conditions rather than assuming that every proposal is well designed.
A harmful parameter change. A proposal changes collateral or liquidation settings in a way that increases exposure during market stress. Independent review, scenario testing, staged implementation where feasible, and post-change monitoring can help identify weaknesses before they become larger problems.
A malicious or misleading proposal. A proposal appears routine but includes an unexpected transfer or permission change. Reviewers should compare the human-readable description with the executable transaction, verify destination addresses, and require independent review for consequential changes.
Low-turnout approval. A proposal passes because few eligible participants vote. Quorum and approval thresholds can help, but they should be assessed alongside historical participation, voting concentration, and the significance of the proposed action.
Compromised administrative credentials. An attacker gains access to a privileged key and attempts to alter contract settings or move funds. Limited permissions, protected signing procedures, independent signers, monitoring, and tested key-revocation processes can reduce the potential impact.
An emergency response that creates new risks. A protocol pauses one function to contain a vulnerability but leaves another exposed, or uses emergency permissions without adequate documentation. Incident procedures should define activation conditions, permitted actions, communications, and a process for reviewing emergency decisions afterward.
No single measure can eliminate governance risk. A timelock may provide review time but cannot make malicious code safe. A vote can establish authorization but cannot guarantee sound implementation. An audit can identify certain weaknesses without proving that every possible failure has been prevented.
A Practical Framework for Evaluating DeFi Governance
Use the following sequence to evaluate a protocol’s governance structure before relying on its stated safeguards.
Step 1: Map the authority structure. Document who can propose, vote, execute, upgrade, pause, and change permissions. Identify any authority held by a foundation, multisignature group, administrator, or development team outside the ordinary voting process.
Step 2: Review voting and participation data. Examine token concentration, delegation patterns, quorum requirements, approval thresholds, historical turnout, and voting records. Distinguish between wallet addresses and independent participants because one entity may control multiple addresses.
Step 3: Trace a consequential decision. Select a completed proposal involving a parameter change, treasury transfer, or contract upgrade. Follow the proposal from discussion through approval and execution. Verify the transaction and resulting contract state against the approved terms.
Step 4: Test technical safeguards. Check for independent code review, testing, timelocks, restricted permissions, monitoring, and documented emergency procedures. Review whether a privileged account can bypass ordinary governance and what limits apply.
Step 5: Assess financial consequences. Determine how the decision could affect collateral quality, liquidity, liquidation capacity, treasury exposure, and users. Test plausible adverse conditions rather than relying solely on expected or average market conditions.
Step 6: Record gaps and escalation routes. Document unverified assumptions, unresolved permissions, missing evidence, and the process for responding to a harmful change. A useful review separates confirmed controls from controls that exist only in documentation.
This framework is not a universal scoring model. Different protocols have different purposes, architectures, and risk tolerances. The objective is to establish whether the governance arrangements are appropriate for the functions they control and whether the available evidence supports that conclusion.
Free educational tool
Are you ready for digital assets?
Seven quick questions on knowledge, mindset and goals, with one honest answer about where you stand.
Educational tool. Results are not investment advice.
Transparency, Accountability, and the Limits of On-Chain Records
Public blockchain records can help reviewers inspect votes, transactions, contract permissions, and certain changes in protocol state. However, transparency does not resolve every governance question.
On-chain data may not reveal private coordination among token holders, conflicts of interest, informal influence over developers, or the identity behind multiple wallets. A public vote also does not guarantee that participants understood the proposal or that the outcome represents every user affected by the decision.
Legal and regulatory responsibilities depend on the arrangement’s activities, control structure, and applicable jurisdiction. A DAO label does not independently determine legal status or remove every obligation that may apply to participants or entities exercising control. The FATF report provides a risk-based regulatory perspective, but jurisdiction-specific questions require separate legal assessment.
Technical safeguards have limitations as well. Smart contracts generally execute according to their programmed logic and permissions. They cannot independently determine whether a governance decision is fair, whether a proposal serves all stakeholders, or whether an emergency intervention is justified.
For further information, see What Are Smart Contracts and How Do They Shape Digital Trading?
Governance participation can also carry operational responsibilities for institutions. Reviewing proposals, monitoring delegated authority, documenting conflicts, and tracking implementation require time and defined oversight.
Recommended Read: Governance Participation as an Institutional Income Stream examines participation and accountability from an institutional perspective.
How To Evaluate DeFi Governance Through Verifiable Controls
Changes to lending parameters, treasury allocations, and smart contract permissions can influence how a DeFi protocol operates under normal conditions and market stress. Evaluating who authorizes these changes, how they are implemented, and what safeguards apply can help you assess governance structures more effectively.
Register Now to access Kenson Investments’ educational resources on digital asset infrastructure, market structure, and risk considerations. Have questions? Speak with our digital asset specialists.
Disclaimer: The information provided on this page is for educational and informational purposes only and should not be construed as financial advice. Crypto currency assets involve inherent risks, and past performance is not indicative of future results. Always conduct thorough research and consult with a qualified financial advisor before making investment decisions.
“The cryptocurrency and digital asset space is an emerging asset class that has not yet been regulated by the SEC and the US Federal Government. None of the information provided by Kenson LLC should be considered as financial investment advice. Please consult your Registered Financial Advisor for guidance. Kenson LLC does not offer any products regulated by the SEC, including equities, registered securities, ETFs, stocks, bonds, or equivalents.”



